Modern work offers unprecedented flexibility, but it has introduced a level of complexity that traditional security models were not built to handle. As organizations adopt generative AI, they are finding that it is not simply another application to manage; it changes an already fragmented operating environment.
Today’s environment spans on-premises infrastructure, public and private clouds, and SaaS. As a Solutions Architect, I see how this complexity strains traditional perimeter security. Organizations must protect employees, contractors, partners and non-human identities such as AI agents and service accounts. With people working from many locations on managed and unmanaged devices, AI security is an infrastructure challenge as well as an application concern.
1. Governance and Cost: The Hidden Killers of AI Innovation
The initial excitement surrounding AI often masks the structural risks that lead to project failure. From an architectural standpoint, the “AI revolution” often stalls because the underlying infrastructure cannot support the necessary governance or the unpredictable nature of Large Language Model (LLM) interactions.
Gartner’s January 2026 analysis reported that at least 50% of generative AI projects had been abandoned after proof of concept by the end of 2025. It cited poor data quality, inadequate risk controls, escalating costs and unclear business value among the causes. Key challenges include:
- Data quality: Poor data quality can undermine project outcomes.
- Risk controls: Inadequate controls can leave risks unmanaged.
- Costs: Expenses can escalate beyond planned budgets.
- Business value: Unclear value can make it difficult to justify continued investment.
To move beyond pilots, organizations need a governed, cost-aware operating model that integrates with their broader security architecture.
2. Your Gateway to “Prompt Governance”
When most organizations think of security, they think of legacy firewalls. However, securing AI requires a shift in focus toward the “Token” and the “Prompt.” This is where the NetScaler AI Gateway redefines the boundary.
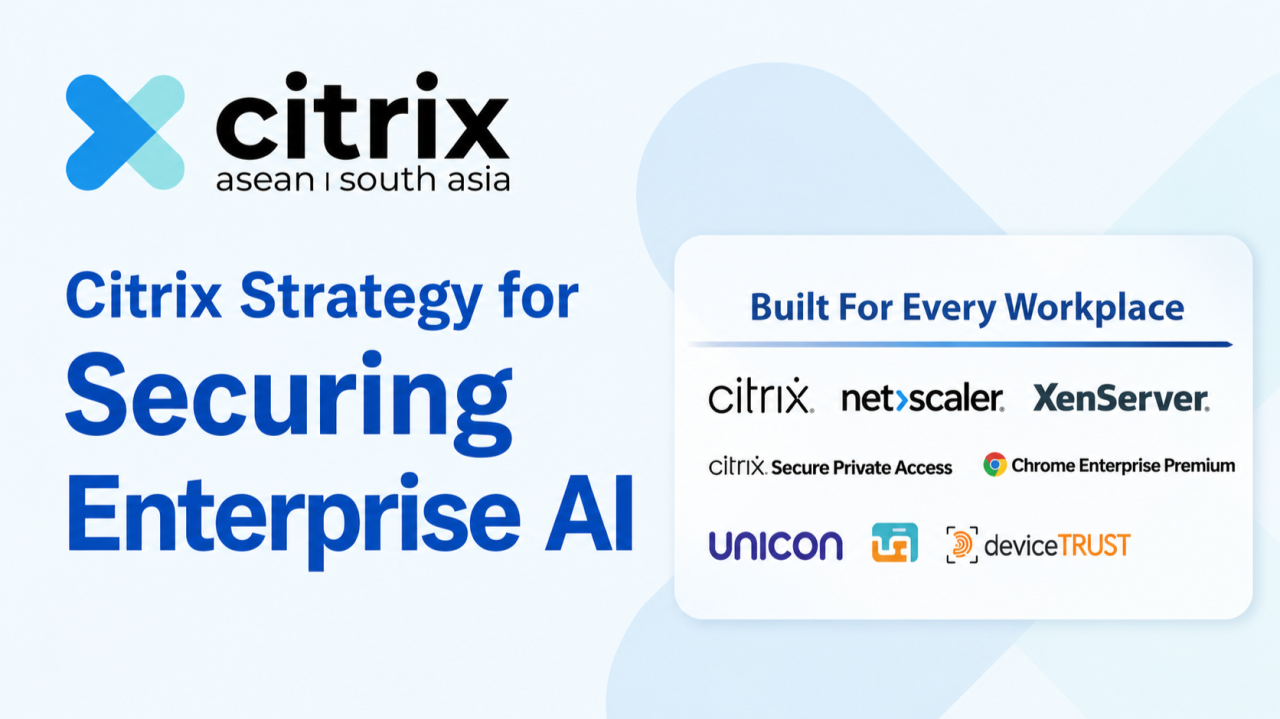
NetScaler AI Gateway provides a control point for enterprise AI traffic. In its July 2026 announcement, Citrix described model routing and token-level usage tracking for LLM traffic, along with MCP Gateway functionality to route, govern and observe agent traffic to MCP servers. Check the release and configuration to confirm which features are available in a specific deployment.
- LLM traffic: Model routing and token-level usage tracking.
- Agent traffic: Routing, governance and visibility for traffic to MCP servers.
AI traffic governance should be combined with the organization’s identity, data-protection and model-safety controls.
3. The Hardened Endpoint: Keeping AI Data Off the Device
In the AI era, the “last mile”—the physical device—is a primary vulnerability. A zero-local-data approach can help reduce exposure. One deployment option combines Citrix DaaS Cloud with Citrix UniconOS, a write-protected endpoint operating system.
Citrix UniconOS can be configured to launch devices directly into a Citrix DaaS Cloud or Citrix DaaS Local (formerly Citrix Virtual Apps and Desktops) session. Its write-protected design and centralized management can help reduce local data exposure. Session policies, including controls for clipboard, printing and drive mapping, can provide additional safeguards; available controls depend on the deployment and its configuration. Validate the settings against the organization’s data-protection requirements.
4. Ephemeral Spaces: Protecting the Hands That Build the AI
Securing the end-user is critical, but we must also secure the “Power User” and “Developer” personas. These creators often require high-level access to training data and model weights, making their environments high-value targets for exfiltration.
Citrix SecurSpaces (formerly Citrix Secure Developer Spaces) provides container-based Cloud Development Environments (CDE). These hosted, ephemeral environments can support AI-assisted development workflows. Their protections depend on configuration, particularly access and egress controls:
- Code and credentials can remain in the hosted environment rather than on the local endpoint, subject to configuration.
- Egress policies can restrict unauthorized data movement to external repositories.
- Ephemeral environments can be removed when no longer needed, reducing persistent access and data exposure.
5. AI is Only as Safe as the Infrastructure It Runs On
True AI security cannot be a bolt-on feature; it must be the foundation of the infrastructure itself. For an organization to realize “operational confidence,” security must follow the data path from the user all the way to the workload.
User → Apps & Tools → Data → Workloads → Visibility
This comprehensive strategy is built on five core pillars:
- Secure Access: Verifying every human and non-human user and device via Zero Trust and adaptive authentication.
- Secure AI Workspace: Isolating AI experiences to prevent data leakage.
- Secure Data: Protecting data in transit using post-quantum-ready ciphers and auditing every interaction via Session Recording.
- Secure AI Workloads: Utilizing XenServer and GPU-enabled virtualization to run training and inference in controlled, private environments.
- Visibility & Threat Detection: Using Citrix Experience Insights (formerly uberAgent) can help teams monitor endpoint activity and investigate suspicious behavior.
Ultimately, the goal is to ensure that innovation does not come at the cost of integrity. As our core philosophy states:
“AI is only as safe as the data it uses and the access it operates with.”
The Future of Confident Innovation
Security should support responsible AI adoption. By combining appropriate access controls, data protections and operational visibility, organizations can advance their AI initiatives while supporting their security and compliance objectives.